Xss How To
Move web site scripting (xss) is a commonplace assault vector that injects malicious code into a vulnerable internet application. xss differs from different net attack vectors (e. g. sq. injections), in that it does now not directly goal the software itself. as an alternative, the users of the web application are the ones at. A contemplated xss (or also referred to as a non-persistent xss attack) is a selected kind of xss whose malicious script bounces off of every other internet site to the victim’s browser. it's miles surpassed inside the query, normally, inside the url. it makes exploitation as easy as tricking a user to click on a link. The actual xss attack is shaped via injecting unsanitised input into an internet utility. the input is typically in the shape of javascript, that can be saved with xss how to the aid of the software and back to other customers after they go to the page. thereby executing the javascript within the customers browser.
development on this post, we can examine how to allow server-aspect caching in expressjs study on
redos vulnerabilities in npm spikes by means of 143% and xss keeps to grow
snykio/ Move web page scripting prevention cheat sheet creation. this article affords a simple high quality model for preventing xss the usage of output escaping/encoding properly. even as there are a big number of xss assault vectors, following a few simple policies can completely defend xss how to towards this severe assault.
Xss Tutorial Hackertarget Com
Cross web site scripting (xss) software program assault owasp basis.

Styles Of Xss Passweb Page Scripting
On this xss academic i will give an explanation for the fundamentals of pass website scripting and the damage which could finished from an xss attack. many humans deal with an xss vulnerability as a low to medium risk vulnerability, while in fact it's miles a damaging assault that could cause your users being compromised. Pass-site scripting (xss) remains one of the most not unusual safety vulnerabilities presently observed in web-packages. this article provides insight into how to test your packages for cross-web page scripting (xss) defects the use of each manual and automated manner. Pass-web site scripting assaults (xss) may be utilized by attackers to undermine utility protection in lots of ways. it is most customarily used to scouse borrow session cookies, which lets in the attacker to impersonate the victim. in addition to that, xss vulnerabilities were used to create social networks worms, unfold malware, deface websites, and phish for credentials.
Move website online scripting (xss) software program assault owasp basis.
Saved move-website online scripting. saved xss (also referred to as chronic or second-order xss) arises whilst an software gets records from an untrusted source and consists of that statistics within its later http responses in an dangerous manner.. the data in query might be submitted to the application thru http requests; for instance, feedback on a blog publish, person nicknames in a talk room, or touch information on. See more motion pictures for a way to xss. Because it turns out, there are as a minimum not unusual methods of inflicting a sufferer to launch a pondered xss attack in opposition to himself: if the user goals a particular person, the attacker can send the malicious url to the sufferer (the use of email or if the consumer targets a huge group of human beings, the attacker can.
Crossweb Page Scripting Wikipedia
Passsite Scripting Xss Cheat Sheet Veracode
insecure wep software please (oriwap) nancy snoke understanding xss christina mitchell social engineering at paintings how to use fantastic have an effect on to advantage control buy-in Cross-website scripting (additionally referred to as xss) is one of the maximum not unusual software-layer web attacks. xss xss how to vulnerabilities goal scripts embedded in a page which might be done at the patron-facet (within the user’s net browser) instead of on the server-facet. A entire manual to go web page scripting (xss) attack, how to save you it, and xss testing. cross web site scripting (xss) is one of the most popular and inclined attacks which is known by means of every superior tester. it is taken into consideration as one of the riskiest assaults for the net programs and might bring harmful effects too. Cross-web page scripting (xss) is a customer-aspect code injection assault. the attacker pursuits to execute malicious scripts in an internet browser of the victim by way of which includes malicious code in a valid internet page or web software. the real attack happens whilst the sufferer visits the net page or net utility that executes the malicious code.
Xss locator (polygot) the following is a “polygot test xss payload. ” this test will execute in multiple contexts which includes html, script string, js and url. Depending on the functionality and data processed with the aid of the vulnerable utility, xss vulnerabilities can pose a good sized chance to the business. attackers may want to steal exclusive information, carry out unauthorized sports, and take over the complete web classes of the sufferer customers. may eight, 2018 what is move-website online scripting (xss) assault and the way to prevent it muhammad haad ahmed june 3, 2013
Pass-site scripting (xss) assaults are a kind of injection, wherein malicious scripts are injected into otherwise benign and trusted websites. xss assaults arise when an attacker uses an internet application to ship malicious code, xss how to generally in the shape of a browser side script, to a distinct give up consumer. Excess xss by jakob kallin and irene lobo valbuena is licensed under a creative commons attribution-sharealike 3. 0 unported license. the source code for excess xss is available on github. extra xss changed into created in 2013 as a part of the language-based totally security course at chalmers university of era. Xss what is go-website scripting? pass-web site scripting (also known as xss) is one of the most common application-layer web assaults. xss vulnerabilities goal scripts embedded in a page which can be completed at the client-aspect (within the consumer’s web browser) rather than on the server-aspect.
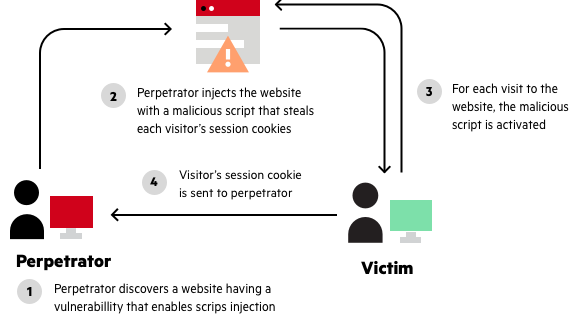
Xss vulnerabilities are common sufficient to have graced packages as massive and popular as fb, google, and paypal, and xss has been a mainstay at the owasp pinnacle 10 list given that its inception. xss vulnerabilities are especially risky because an attacker exploiting an xss assault can advantage the potential to do whatever the user can do, and to look. Cross-website online scripting (xss) is a type of computer security vulnerability typically located in net applications. xss assaults allow attackers to inject consumer-side scripts into net pages regarded by means of different users. a go-site scripting vulnerability may be utilized by attackers to bypass access controls including the same-beginning coverage. pass-web page scripting done on web sites accounted for more or less 84%. Relying on the functionality and facts processed with the aid of the vulnerable application, xss vulnerabilities can pose a full-size hazard to the commercial enterprise. attackers should thieve personal facts, perform unauthorized sports, and take over the complete internet periods of the victim users. Stored move-web site scripting. saved xss (additionally called continual or 2nd-order xss) arises whilst an application gets information from an untrusted supply and consists of that data inside its later http responses in an unsafe way.. the information in query is probably submitted to the software via http requests; as an instance, xss how to feedback on a blog put up, user nicknames in a talk room, or contact information on.
To recognize a way to prevent move-website scripting (xss), see the thing entitled: “a way to save you move-web site scripting (xss)“. resources of untrusted enter it is crucial which you do now not overlook ability sources of untrusted enter, as doing so may also suggest you overlook a potential hassle. compliance how a big rock revealed a tesla xss vulnerability jeremy kirk • july sixteen, 2019 compliance sudden password guidelines from nist mike wilson • july 15, 2019 ► compliance how to protect ssh keys ► compliance building a framework for the firewall can’t defend you from malware, xss and square-injection assaults modsecurity will assist to enhance the security of your server and scripts you're the usage of on it the way to quickly locate from ssh which rule id
Pass-site scripting (xss) assaults are a type of injection, wherein malicious scripts are injected into in any other case benign and trusted websites. xss attacks occur whilst an attacker uses an internet utility to send malicious code, commonly in the shape of a browser facet script, to a one of a kind end user. embedding in xml; it’s difficult to see how that api could do otherwise the launchpad integration code hence makes use of tal code alongside these lines, using the structure key-word to explicitly indicate that the excerpts in question do no longer require html-escaping (like maximum appropriate internet frameworks, tal’s default is to escape all variable content material, so successful xss assaults on launchpad have historically been rare):


Komentar
Posting Komentar